Official Website link
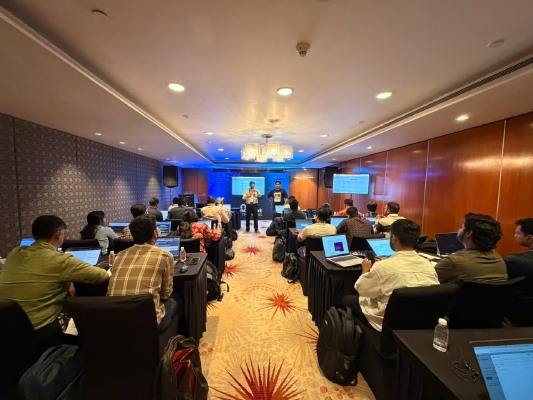
Date: October 27-28, 2026 | 2 Day Training
Location: Jupiter 1, Sheraton Grand at Brigade Gateway, Bengaluru
Track: PenTesting
Format: 2 Day Training
Skill Level: Intermediate to Advanced
Trainers: Anant Shrivastava (Founder, Cyfinoid Research) and Riyaz Walikar (Security Researcher & Offensive Security Expert)
Course Overview
Cloud breaches rarely come from a single isolated mistake. Real attackers chain small weaknesses across exposed services, identity systems, metadata endpoints, storage, serverless functions, managed databases, containers, Kubernetes clusters, developer platforms, and over-privileged integrations until they reach sensitive data or control-plane access. With AI services now native to all major cloud platforms, natural language input widens that exposure further.
Attacking Multi-Cloud Environments and Cloud AI Services is an intensive 2-day hands-on training on practical cloud attack chains across AWS, Google Cloud, Azure, and developer platforms like Railway and Vercel. The course builds a reusable attacker mindset rather than provider-specific theory: students learn which attack ideas are common across platforms, where provider-specific behavior matters, and how small configuration decisions become full compromise paths.
Students deploy vulnerable targets into their own cloud accounts using provided Terraform projects, then work through guided scenarios covering reconnaissance, SSRF, IAM abuse, serverless attacks, managed databases, Kubernetes pivots, AI services and Agentic integration abuse, and developer platform compromise. Each attack path is paired with defensive guidance so students leave with both practical exploitation experience and hardening strategies.
What Students Learn
- Understand realistic multi-cloud attack chains and compromise paths
- Exploit SSRF, metadata services, IAM weaknesses, and cloud misconfigurations
- Approach attacking AI services exposed via Agents and Apps using malicious inputs
- Identify AI Service and Agent integration abuse and over-privileged cloud workflows
- Pivot through serverless, containers, Kubernetes, and developer platforms
- Implement practical hardening and cloud defense strategies